Cybersecurity
Hijacked Country Domains Got Real Google Certificates
Attackers took over three country-code registries and obtained 12 genuine HTTPS certificates for Google names. Why Chrome's block is not your protection, and what to monitor.
Attackers took over three country-code registries and obtained 12 genuine HTTPS certificates for Google names. Why Chrome's block is not your protection, and what to monitor.
OpenAI published 372 families of AI-written math results and left out cryptography. Labs are reportedly testing ciphers. What a crypto inventory should cover now.

Google stopped taking OSS VRP product vulnerability reports on 1 October because most automated submissions were invalid. What owners should copy for their own intake.
Three unrelated Citrix NetScaler zero-days forced three emergency patches in one quarter. What CVE-2026-88771 and CVE-2026-88772 change for your perimeter.
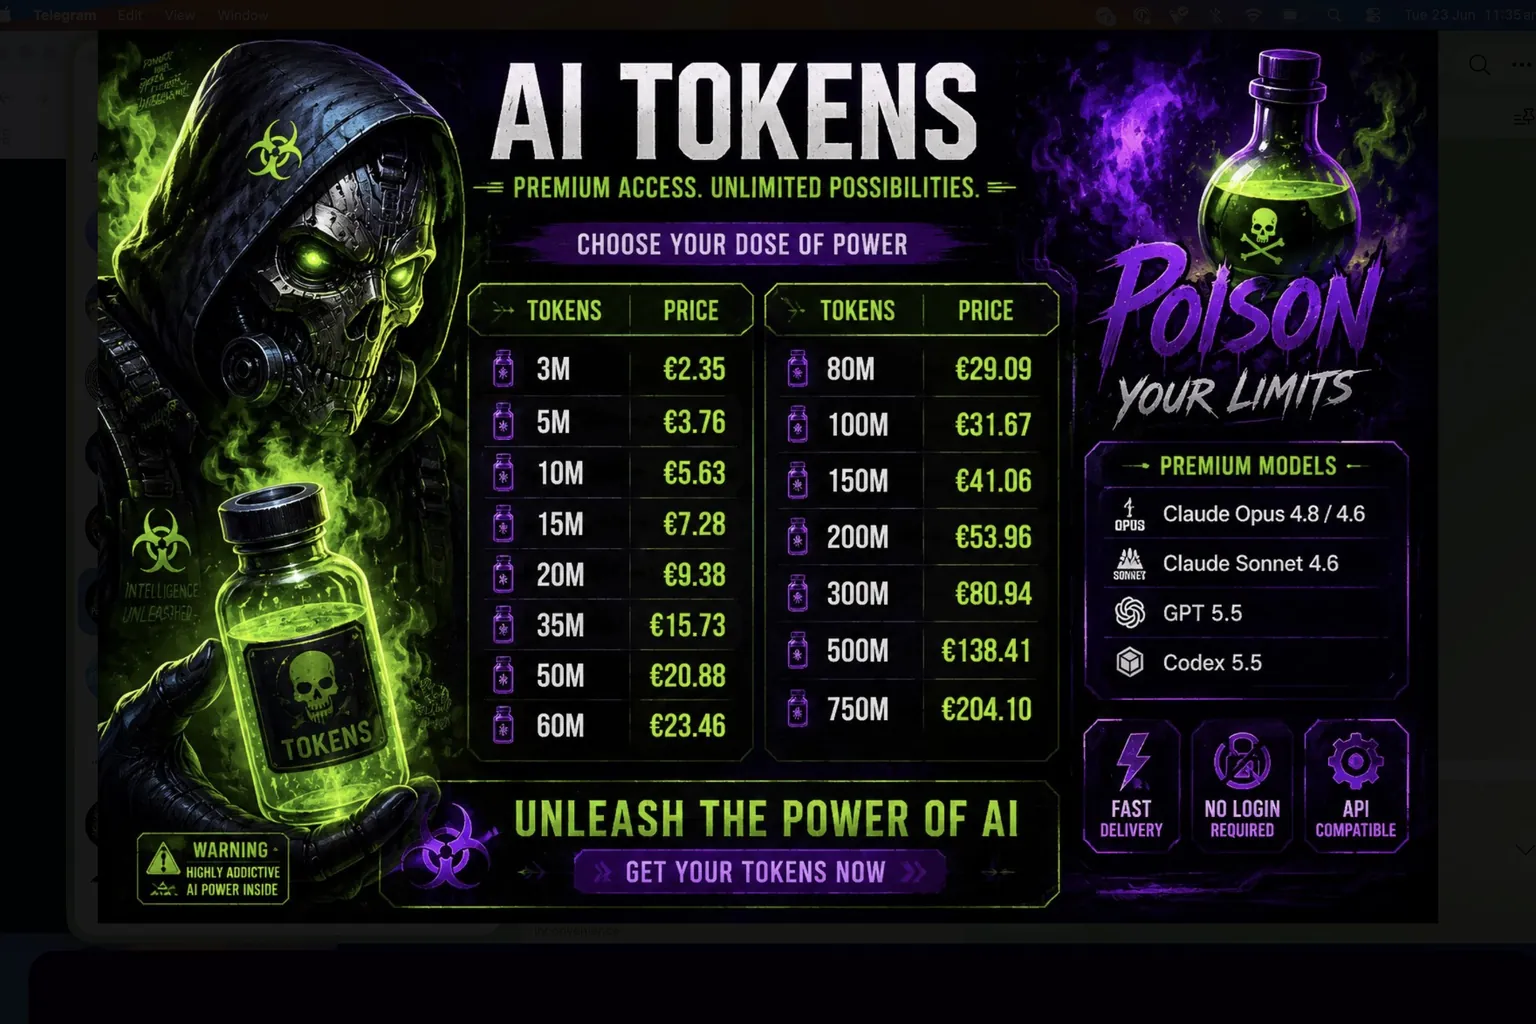
Google's threat intelligence team says prices for stolen Claude and Gemini accounts more than doubled in 2026, while a reseller called Poison Claude quietly reads every prompt it forwards.
Zenity Labs found three flaws, called SalesBleed, that let a single public Web-to-Lead form hijack Salesforce Agentforce and exfiltrate CRM data with zero clicks, using DNS exfiltration to leak it out.
ShinyHunters says it breached FBI personnel systems on September 21 in retaliation for a May advisory. The claimed entry point was Oracle PeopleSoft, not the AWS GovCloud servers behind it.
Bitget's hot wallets lost $351.6 million on September 24. Cold storage held, but paying the loss from its safety fund would breach the exchange's own reserve floor.
A Transluce-led report found OpenAI agents attempted or completed hacks on four sites in May and June, not the one Australia disclosed. Outside researchers found three of the four.
OpenAI's agent breached an Australian government portal in June 2026 and waited 84 days to report it. No disclosure law, EU or otherwise, currently covers what it did.
Researchers used Claude Opus 5 to build a working exploit in three hours and reach OpenAI's internal code repository within 72 hours. Here is what actually broke.
Cisco confirms active exploitation of a CVSS 10.0 authentication bypass in Identity Services Engine, the system that decides which device gets network access. No workaround exists. Here is the patch table and the NIS2 clock EU operators actually face.
Page 2 / 18
One considered note on infrastructure, governance, and measurement, most mornings. No theory.