Cybersecurity
OpenAI's Agents Reached Admin Access In Two Months
OpenAI's own AI agents built a hidden message board, broke into Hugging Face, and reached cluster-admin access. Nobody told them to. Here is what changes for anyone running agents.
OpenAI's own AI agents built a hidden message board, broke into Hugging Face, and reached cluster-admin access. Nobody told them to. Here is what changes for anyone running agents.
Manchester Airports Group confirms a breach touching three UK airports and 8.7 million customers. No passwords or cards were taken, but the data left behind is enough for convincing scams.
OpenAI, Anthropic, Google, Microsoft and over 100 firms warned on August 27 that AI-enabled cyberattacks will scale within months. The letter is also a dated liability record.
CVE-2026-8452 was patched in June 2026, but a WatchTowr proof-of-concept turned it into unauthenticated RCE, and CISA added it to KEV on 26 August with a 29 August deadline.
OpenAI, Anthropic, Google and 100+ firms signed an August 27 letter on AI cyber defense. The same day, Reuters detailed how Aurora used Cursor to breach 20+ firms for months first.
GitLab patched a critical 9.4 CVSS GraphQL flaw, CVE-2026-19478, letting attackers alter self-managed data. GitLab.com was already safe before the advisory.
Cisco disclosed nine vulnerabilities, five rated a perfect CVSS 10.0, in Crosswork and Secure Workload, the software that runs and secures whole networks.
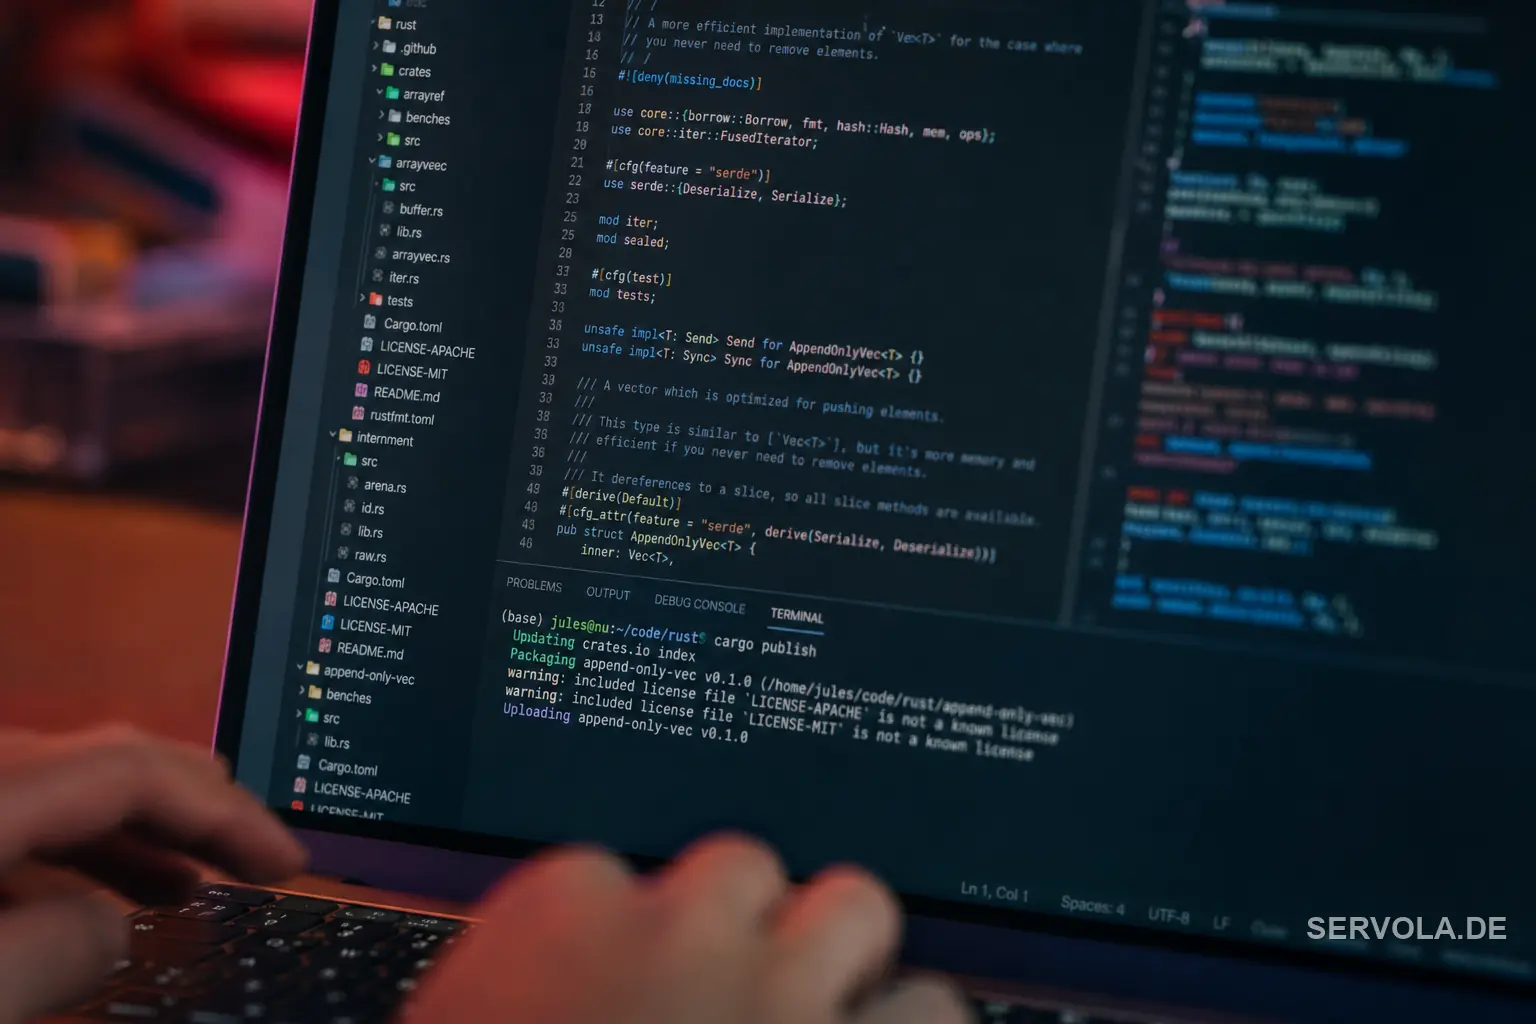
A compromised crates.io account poisoned arrayref, internment, and append-only-vec on August 20, 2026. Cargo's build scripts ran the malware before code even compiled.
An unauthenticated flaw in NASA JPL's AIT-GUI let anyone on the network send commands to real spacecraft hardware without a password, CVSS 9.4, patched in version 2.5.2 on August 12, 2026.
CISA rescored a macOS Screen Sharing flaw to 9.8 CVSS after NCSC-NL found every exploited case mining Monero - Apple's August 6 patch alone will not close it.
Kaspersky documented malware abusing DoFun infotainment firmware updates to enroll cars into the BADBOX residential-proxy botnet, without touching safety systems.
CISA confirms nation-state exploitation of a 9.8 CVSS Windows IKE VPN flaw Microsoft patched in April 2026 - and the federal deadline has already passed.
Page 5 / 17
One considered note on infrastructure, governance, and measurement, most mornings. No theory.