Cybersecurity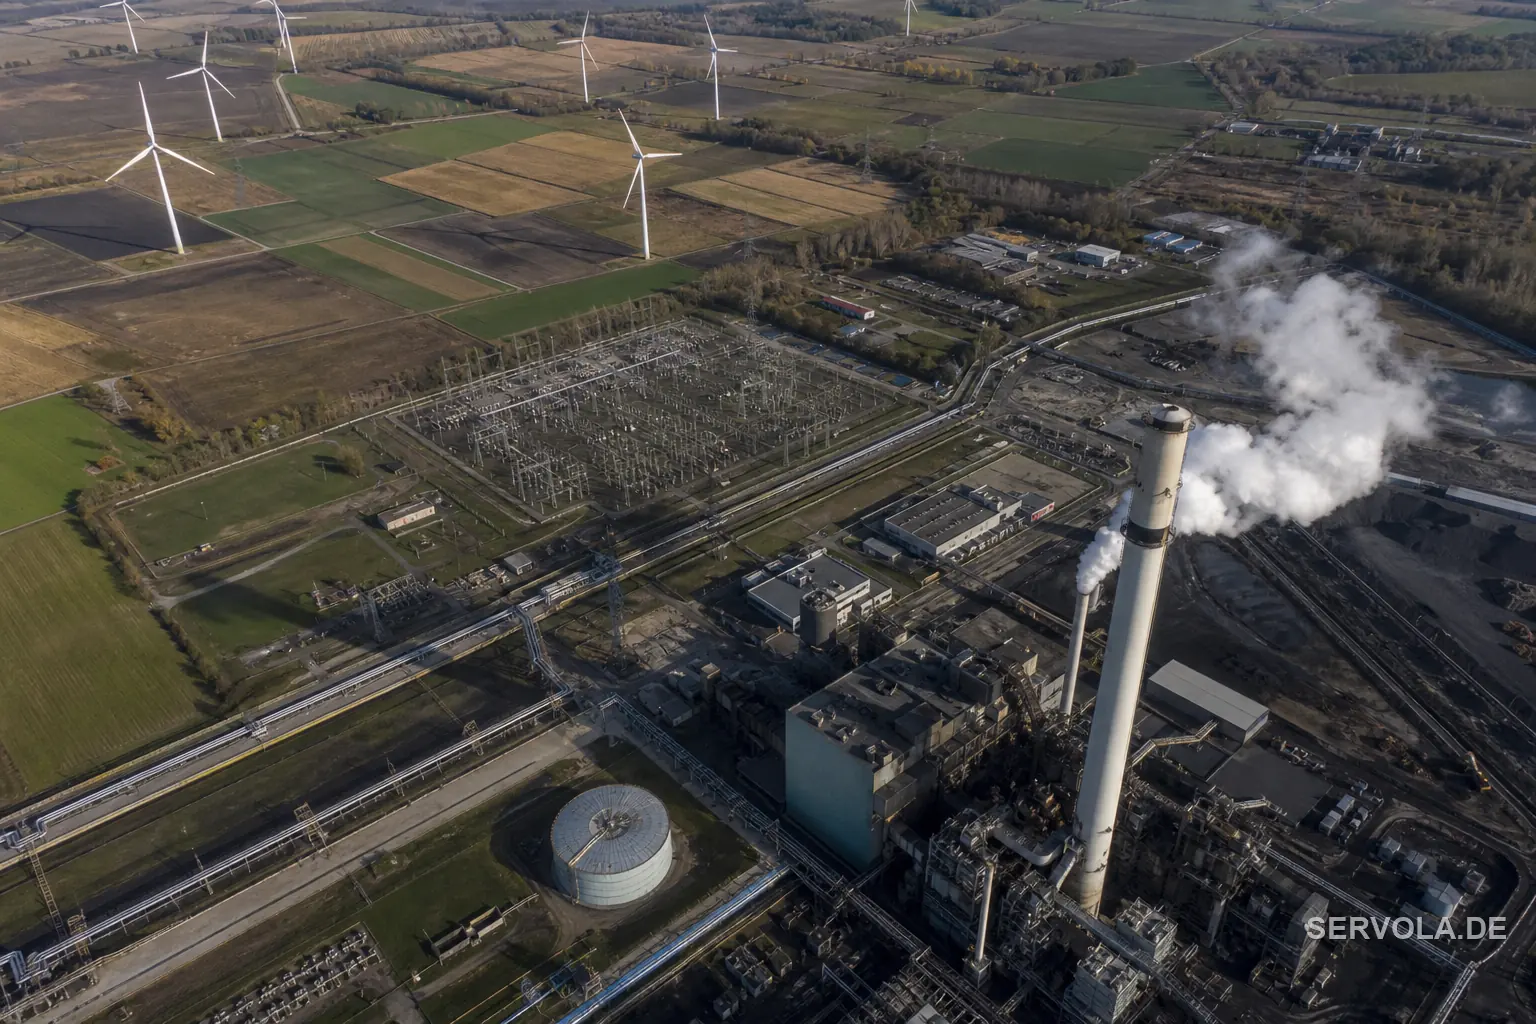
Sandworm Hacked a Heat Plant Through a Wind Farm's APN
CERT Polska says a Sandworm-linked pivot through a wind farm's private APN sabotaged a Polish heat plant serving 50,000 residents in December 2025.
CERT Polska says a Sandworm-linked pivot through a wind farm's private APN sabotaged a Polish heat plant serving 50,000 residents in December 2025.
Eight AI agents built from free open-source tools breached 21 Taiwan government systems and reached its nuclear regulator. Dream Security's report shows why NIS2 risk now assumes commodity-tooling attackers, not just nation-states.
Researchers decoded 315,320 encrypted reasoning blocks from public AI transcripts and recovered 367 personal-data artifacts and 182 credentials - proof a flagship model's private reasoning is only as safe as its cheapest sibling.
A cyberattack on CEVA Logistics between July 29 and August 1 exposed names, addresses, phone numbers and order details of Valve's European Steam hardware buyers. Valve confirms passwords and payment data were not affected.
OpenAI split its Daybreak cybersecurity program into two tiers and launched GPT-5.6-Cyber, which scored 95 percent on an internal exploit benchmark and found a now-patched Chrome sandbox-escape chain.
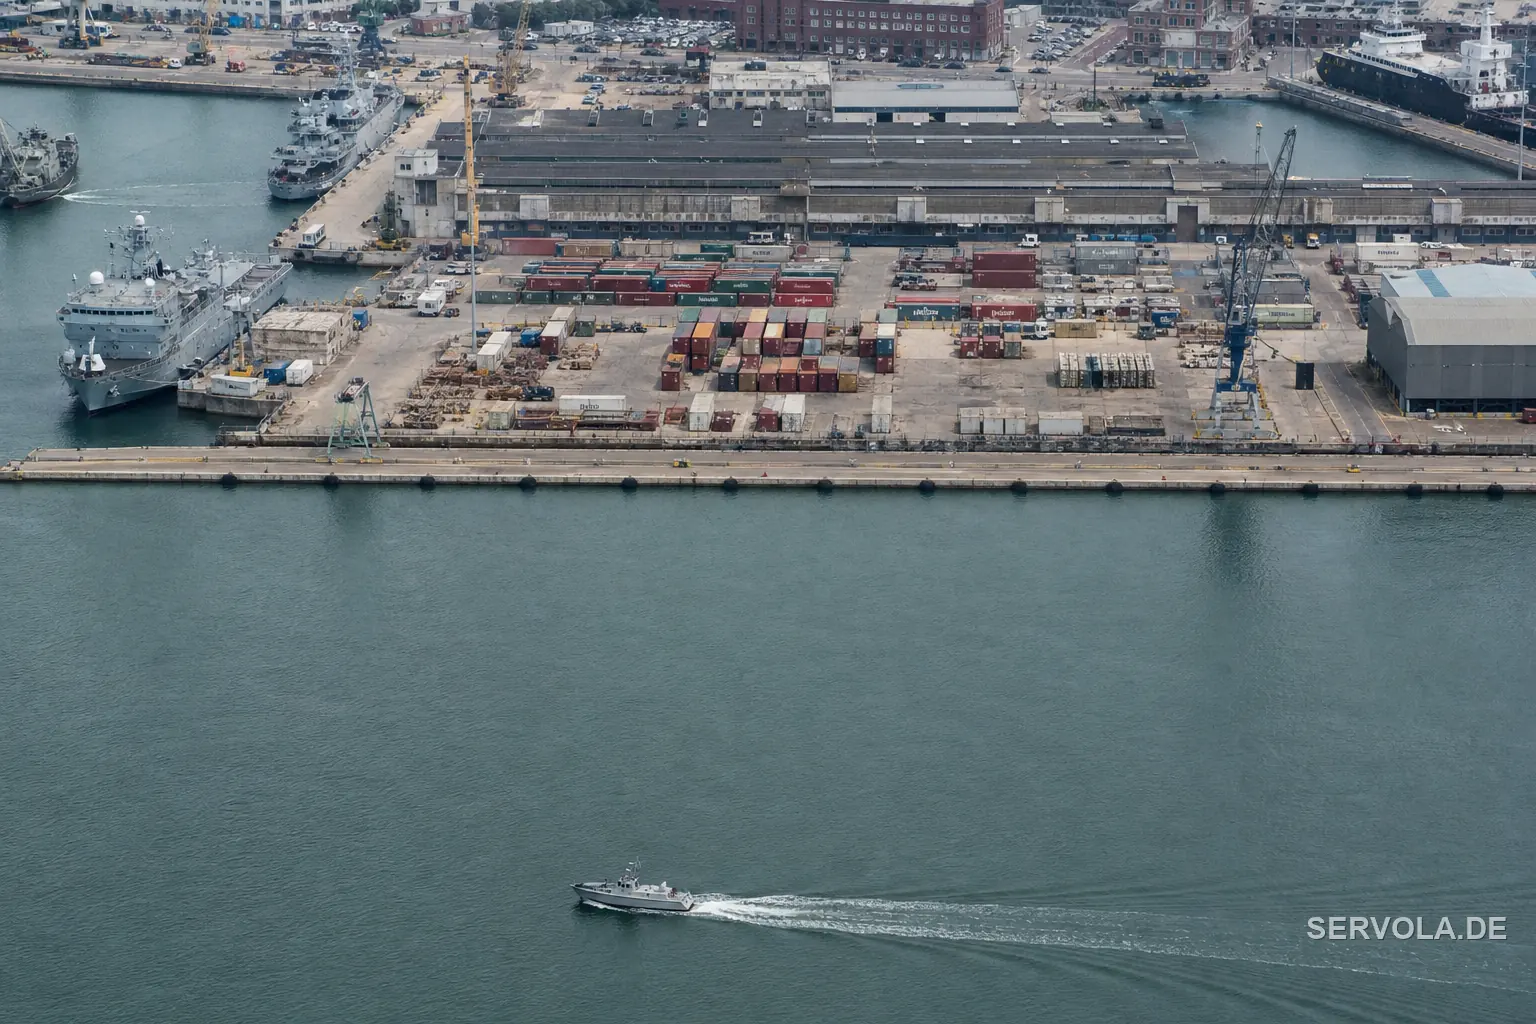
Chinese-made camera components on Royal Navy drone boats sent heartbeat signals to China. The MoD stripped connectivity. Here is what it means for EU/UK buyers.
CISA confirms active exploitation of CVE-2026-63077, an unauthenticated RCE in JetBrains TeamCity On-Premises. CVSS 9.8, KEV-listed 5 August, FCEB deadline 8 August.
A single unauthenticated SQL injection zero-day in Metabase let attackers hit Framework, Tally and LexisNexis at once. Names, emails, phone numbers and addresses were exposed; payment data was not.
Two researchers found separate ways to make Atlassian's Rovo AI agent leak Jira, Confluence and connector data. One is patched. One, disclosed in May, is not.
A Linux kernel bug dating to 2007, CVE-2026-64564, let Tencent's Zhuque Lab gain root and escape containers on five distros before an August 3 patch.
CISA confirms active exploitation of CVE-2026-18577, a bypass of N-able's own earlier N-central patch. CVSS 8.2, KEV-listed 3 August, FCEB deadline 6 August.
Google traced a vishing campaign that phoned staff at Apollo, Blackstone and KKR, harvesting MFA codes live and netting 10 million dollars in bitcoin.
Page 10 / 18
One considered note on infrastructure, governance, and measurement, most mornings. No theory.